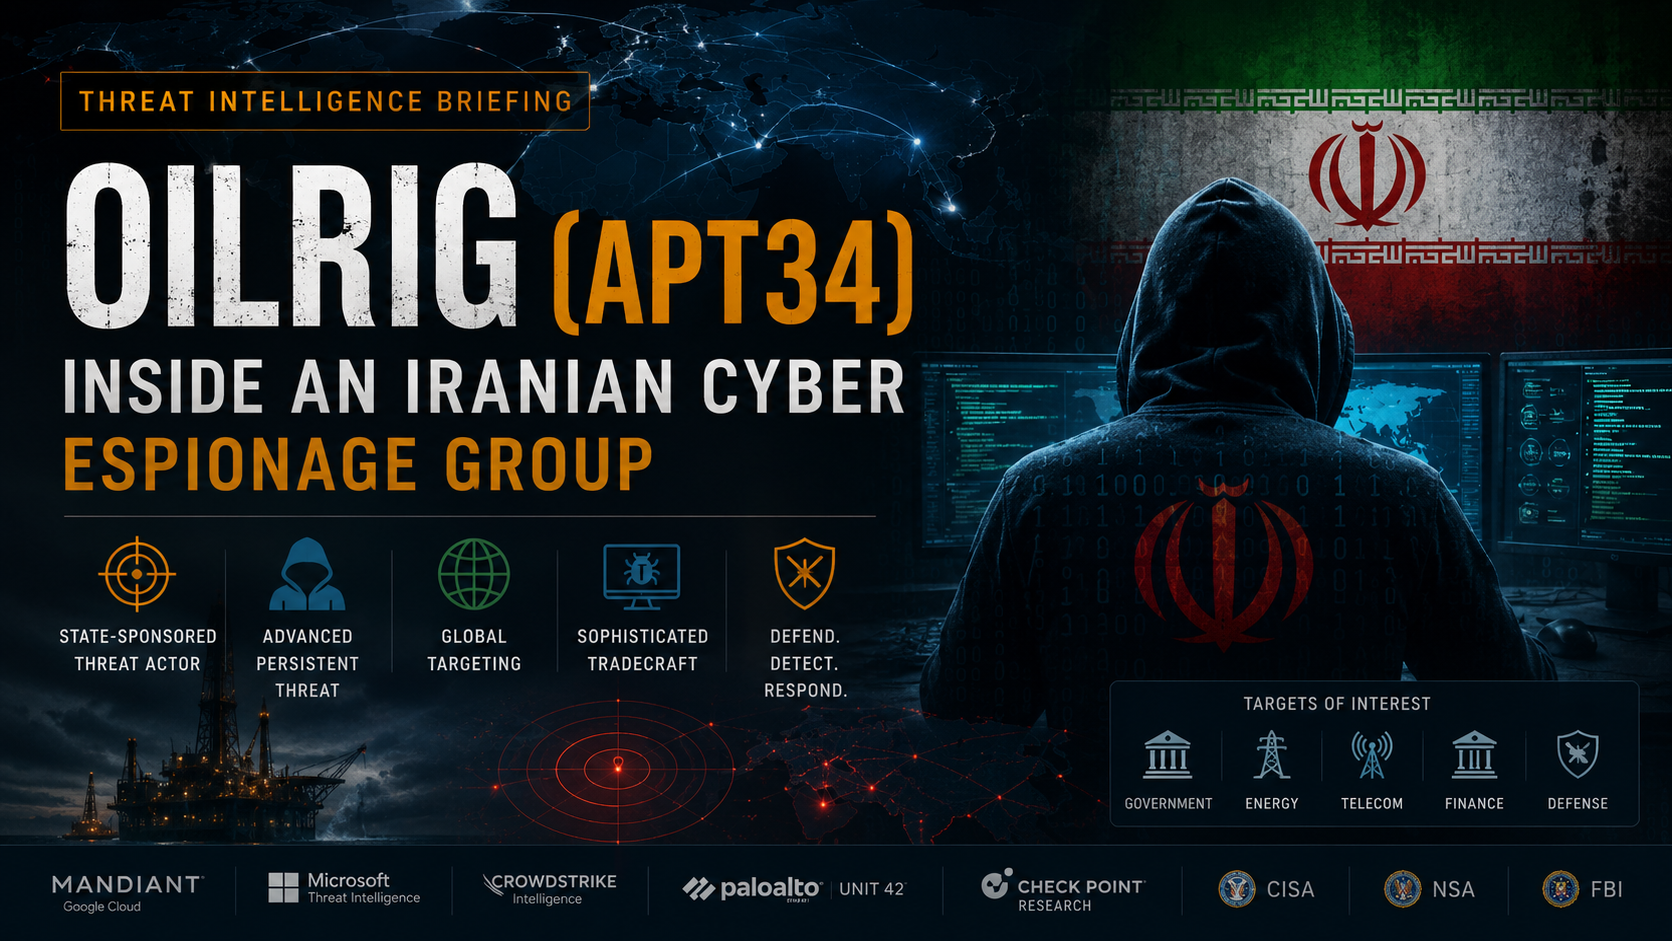
 This video provides a structured overview of OilRig (APT34), an Iranian state-aligned Advanced Persistent Threat (APT) group known for conducting long-term cyber espionage campaigns targeting government organizations, critical infrastructure, energy, telecommunications, finance, and other strategic sectors. The briefing examines the group's identity, motivations, capabilities, attack lifecycle, malware ecosystem, command-and-control techniques, victim targeting, and defensive considerations. It also explores OilRig's tradecraft using the MITRE ATT&CK® framework and the Lockheed Martin Cyber Kill Chain®, helping viewers understand how the group operates and how organizations can strengthen their detection and defense capabilities. This presentation was originally developed as part of a Cyber Threat Intelligence course project and has been further refined into a comprehensive educational briefing using publicly available information from authoritative industry and government sources.
Select your language